Every request, decision and refusal
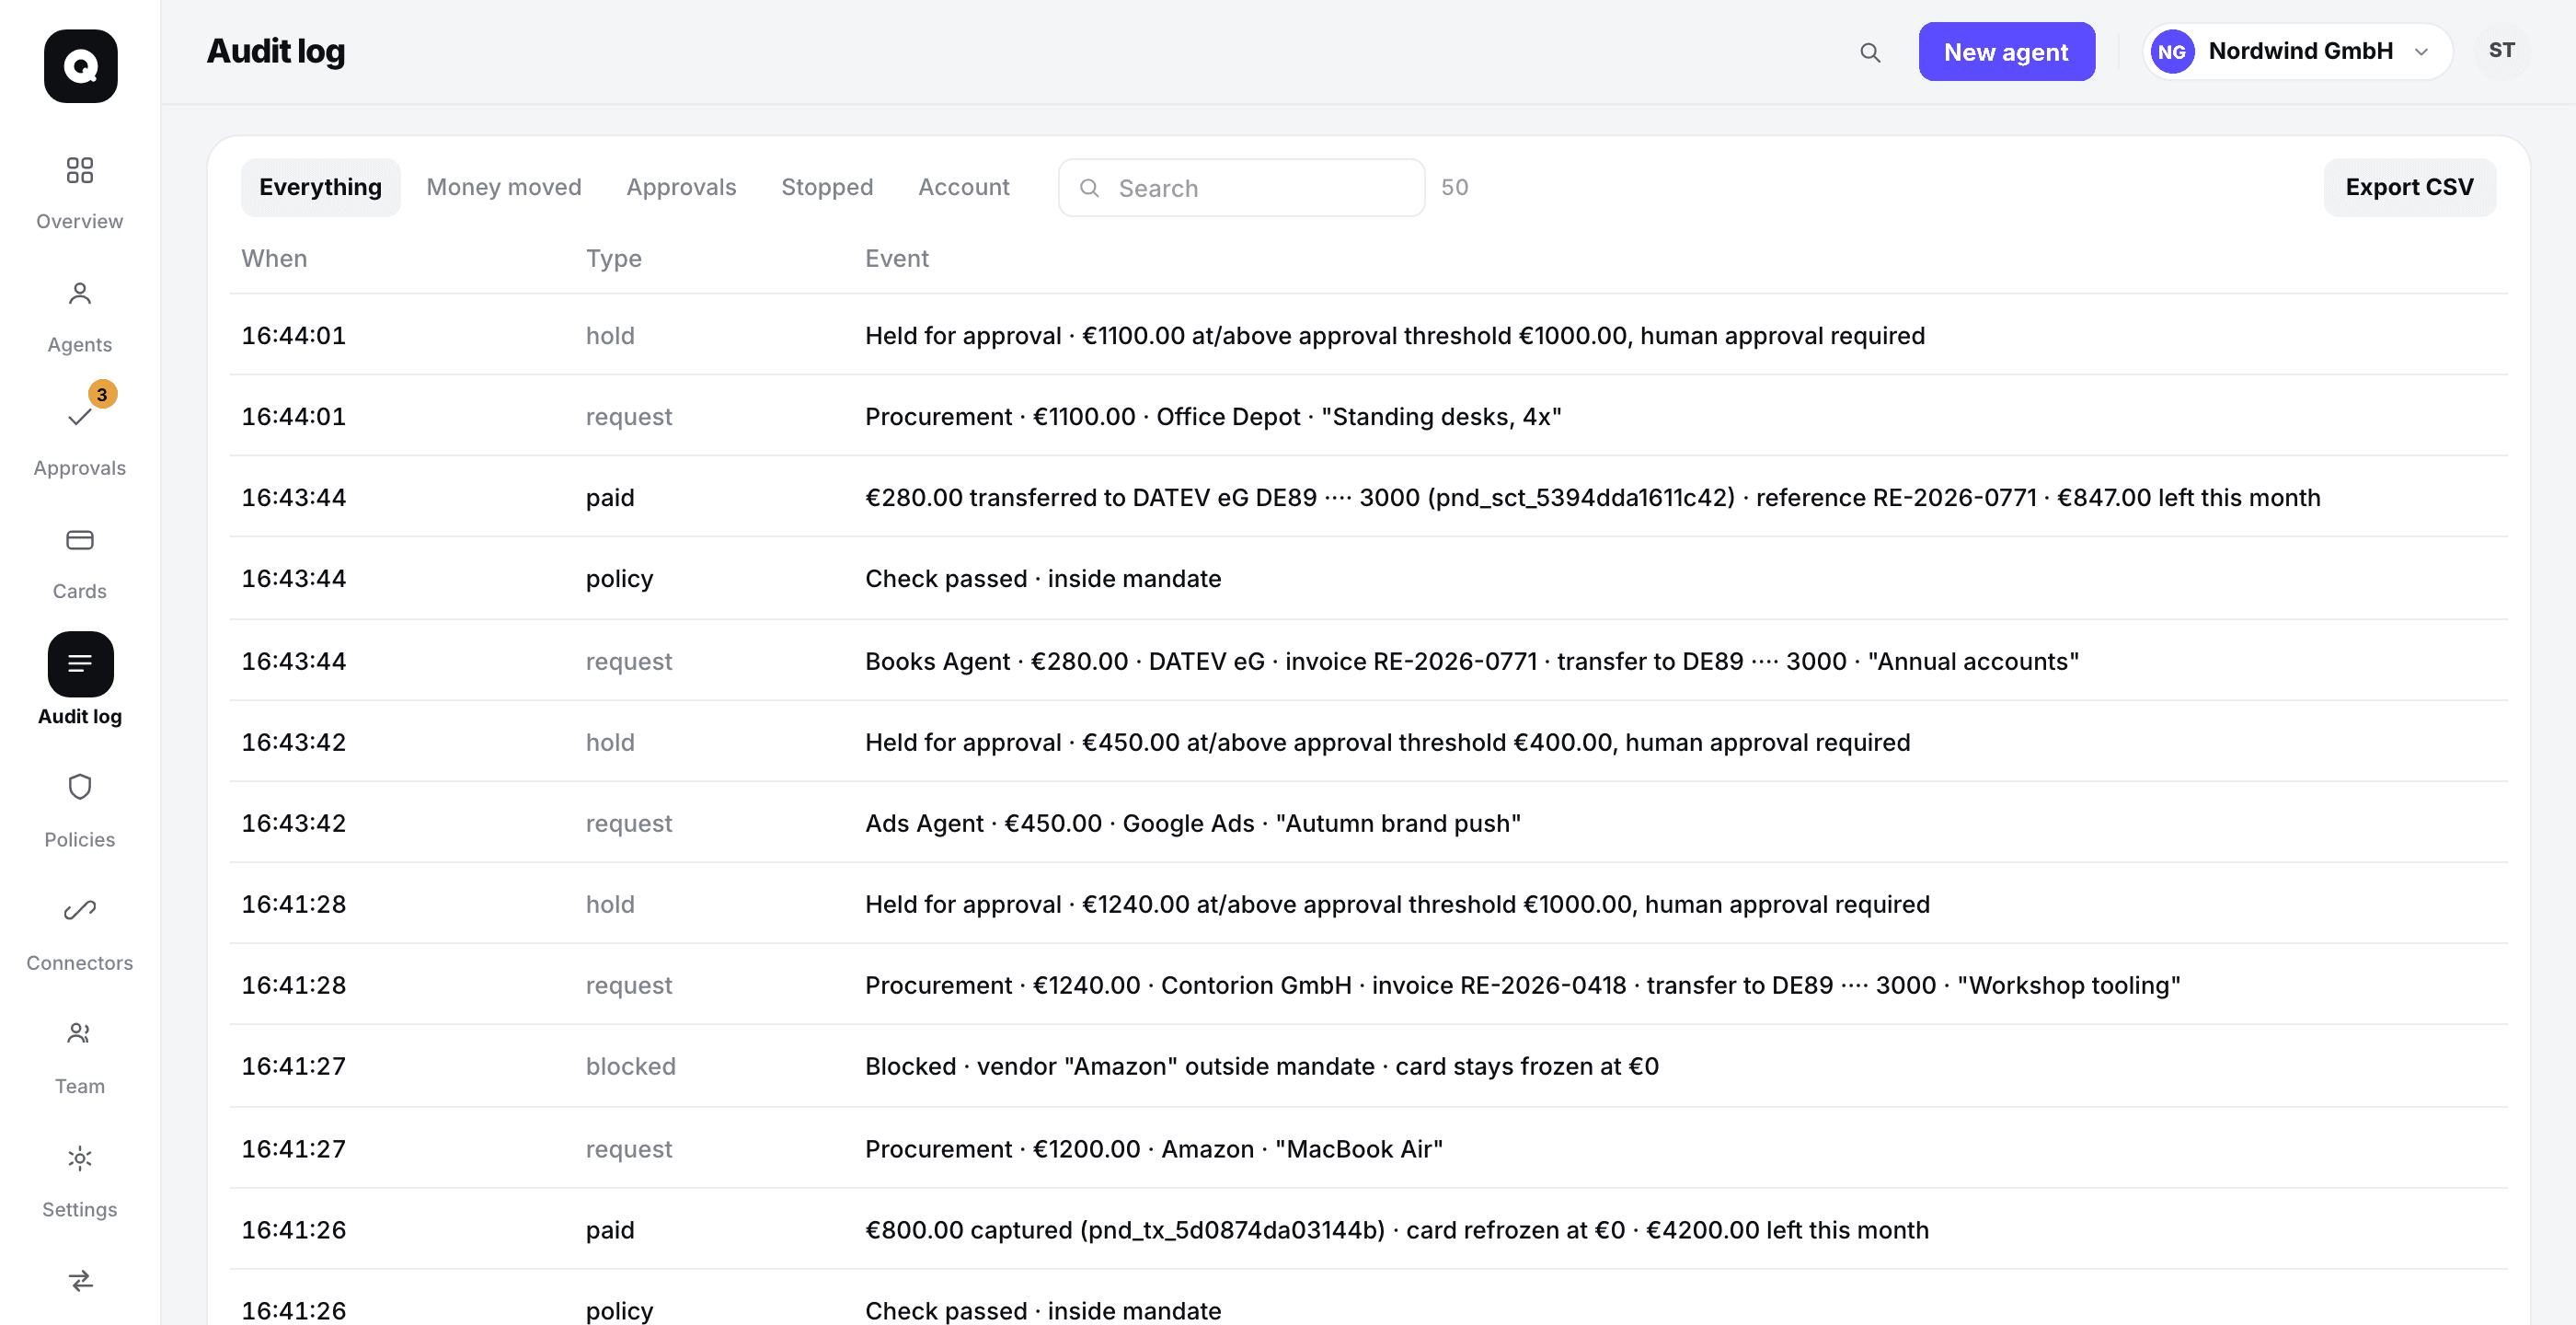
Including the ones that never became a payment. The log is only ever added to, so two exports taken a month apart agree about what happened.
- Requests
- every one
- Policy checks
- passed and failed
- Approvals and declines
- with the rule
- Payments
- with the reference
- Rows that can be edited
- 0
The refusals are the point
A log that only shows what happened tells you nothing about what was stopped. Every blocked request is in here with the rule that blocked it, the vendor that was outside the mandate, and the amount that crossed a ceiling.
Filterable, and it leaves the building
Everything, money moved, approvals, stopped, account. Export is CSV, the format your accountant already has a folder for.
Written for the people who ask later
Accountants, auditors and the EU AI Act all ask the same question after the fact: who authorised this, under what rule, and when. Answering it was the reason to write the log the way it is written.
Questions people ask about this
Can anything be removed from it?+
No. The log is append-only. Archiving an agent or replacing a token does not touch what is already in there.
How far back does it go?+
To the first request in your workspace. Nothing is rolled off.
Can I get it out of Quaestrum?+
CSV export, at any time, with every request, decision and refusal in it.